
Cyber security sales objections, and how to handle them
Selling cyber security means talking to people who are busy, sceptical and already running plenty of tools. These are the objections sales teams hear most often from CISOs, security operations, finance, IT, compliance and engineering leaders. Each one comes with a short video, the thinking behind the objection, and words you can use on your next call.
Objection map
| Objection | Who says it | One way in |
|---|---|---|
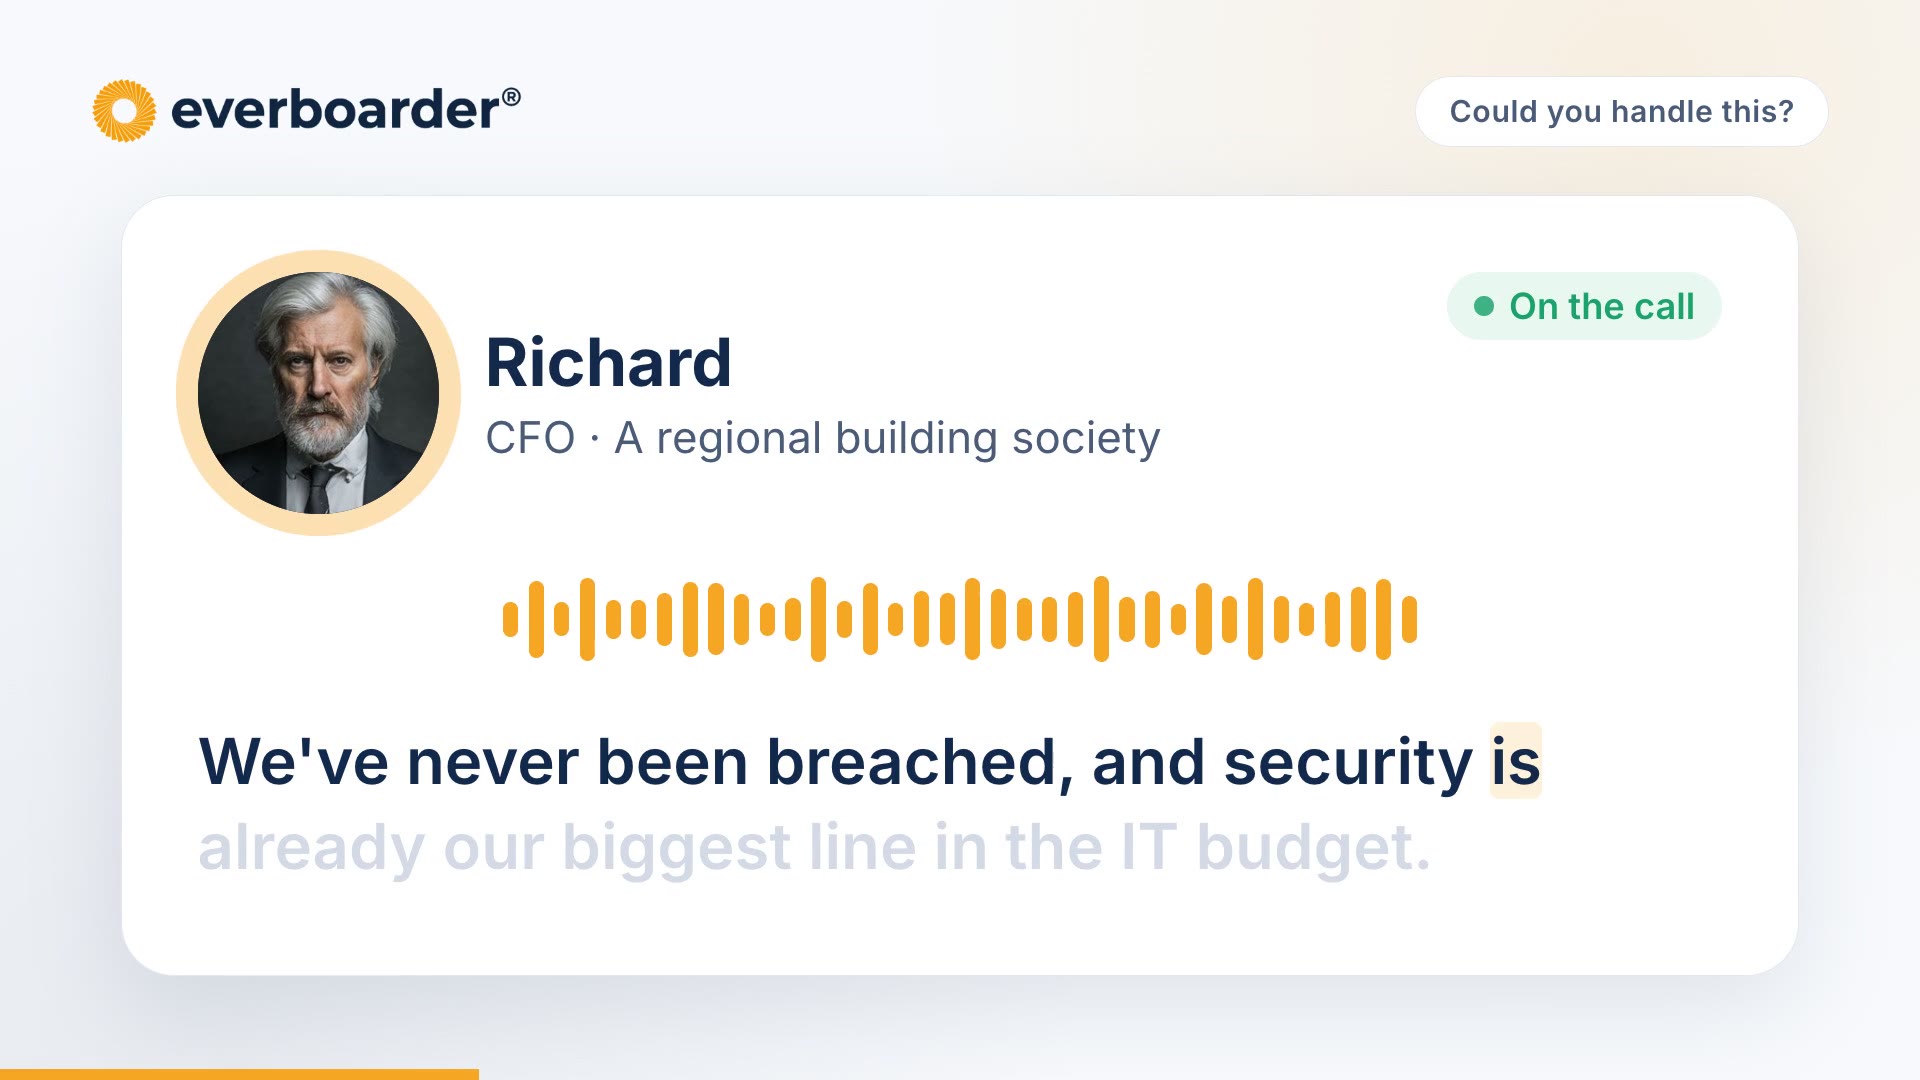
| “We've never been breached” | CFO | Talk in their numbers. |
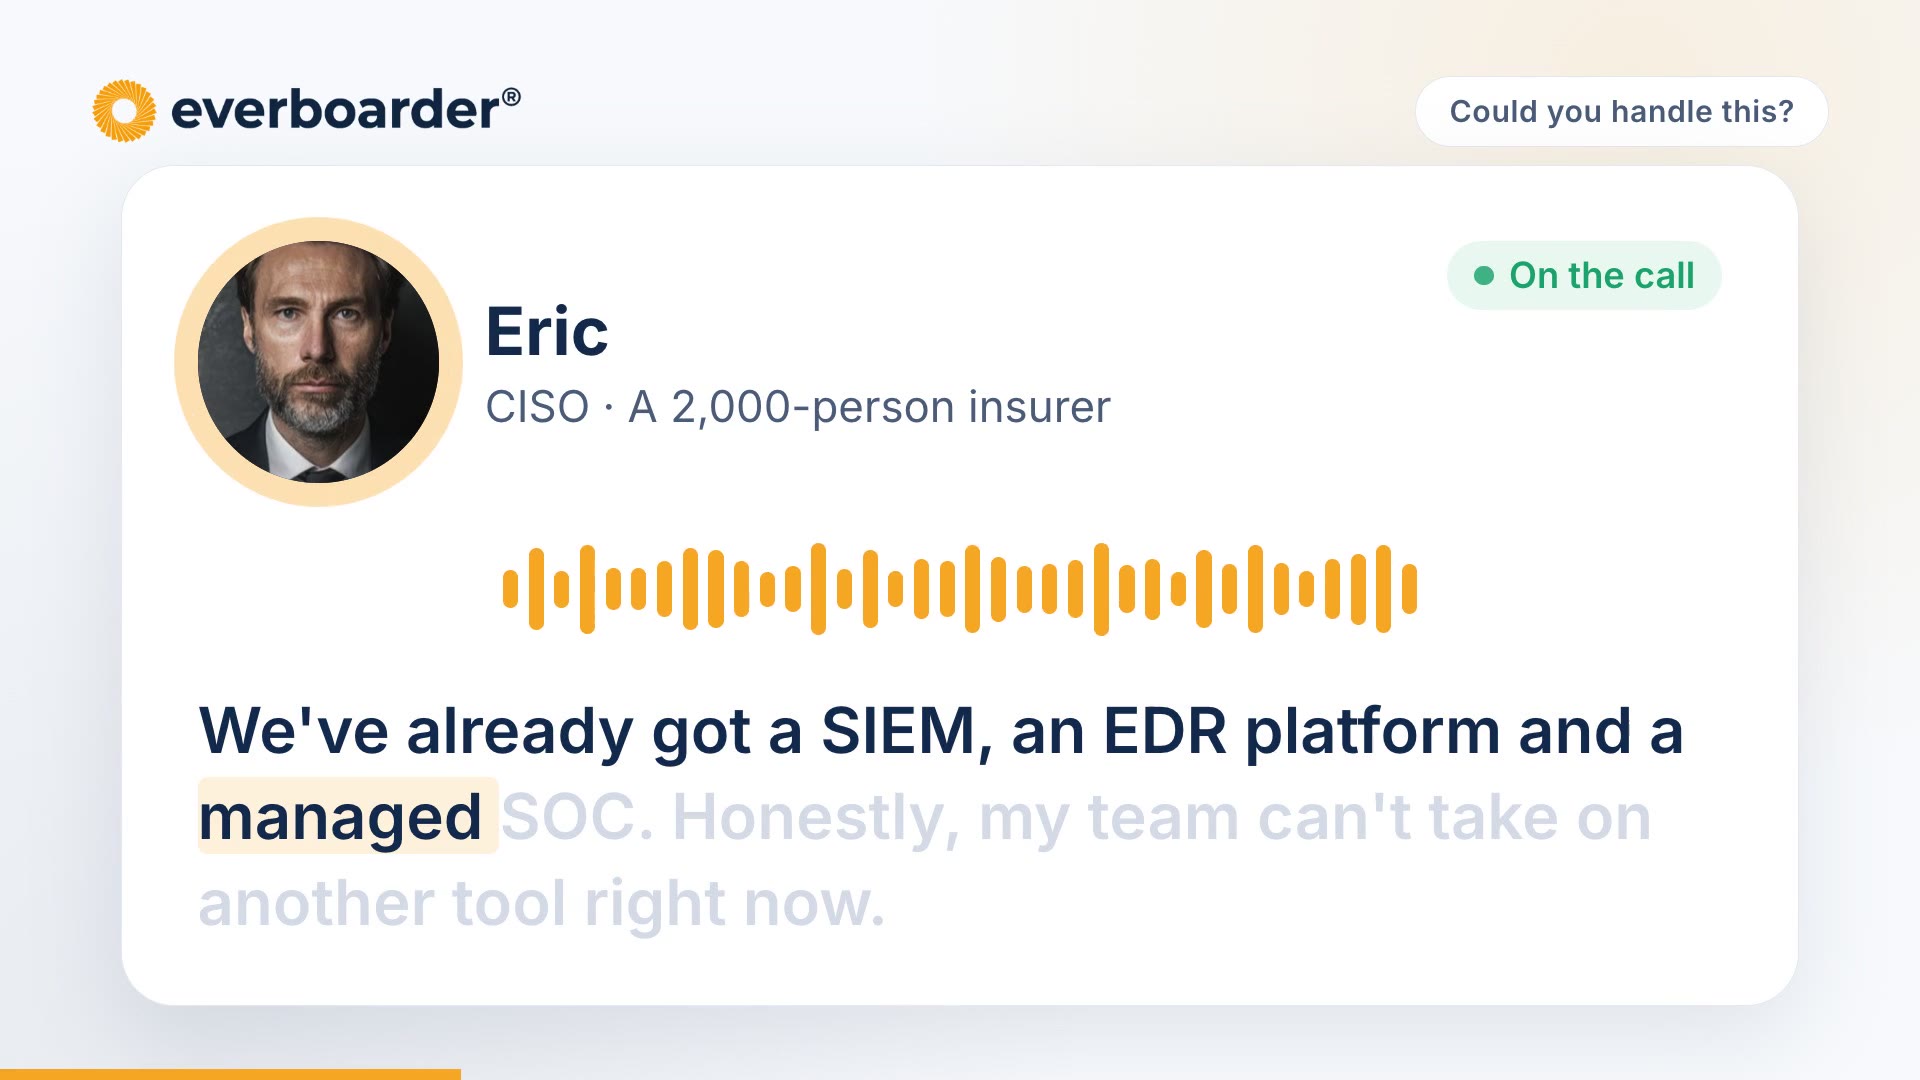
| “My team can't take on another tool” | CISO | Don't defend. Explore. |
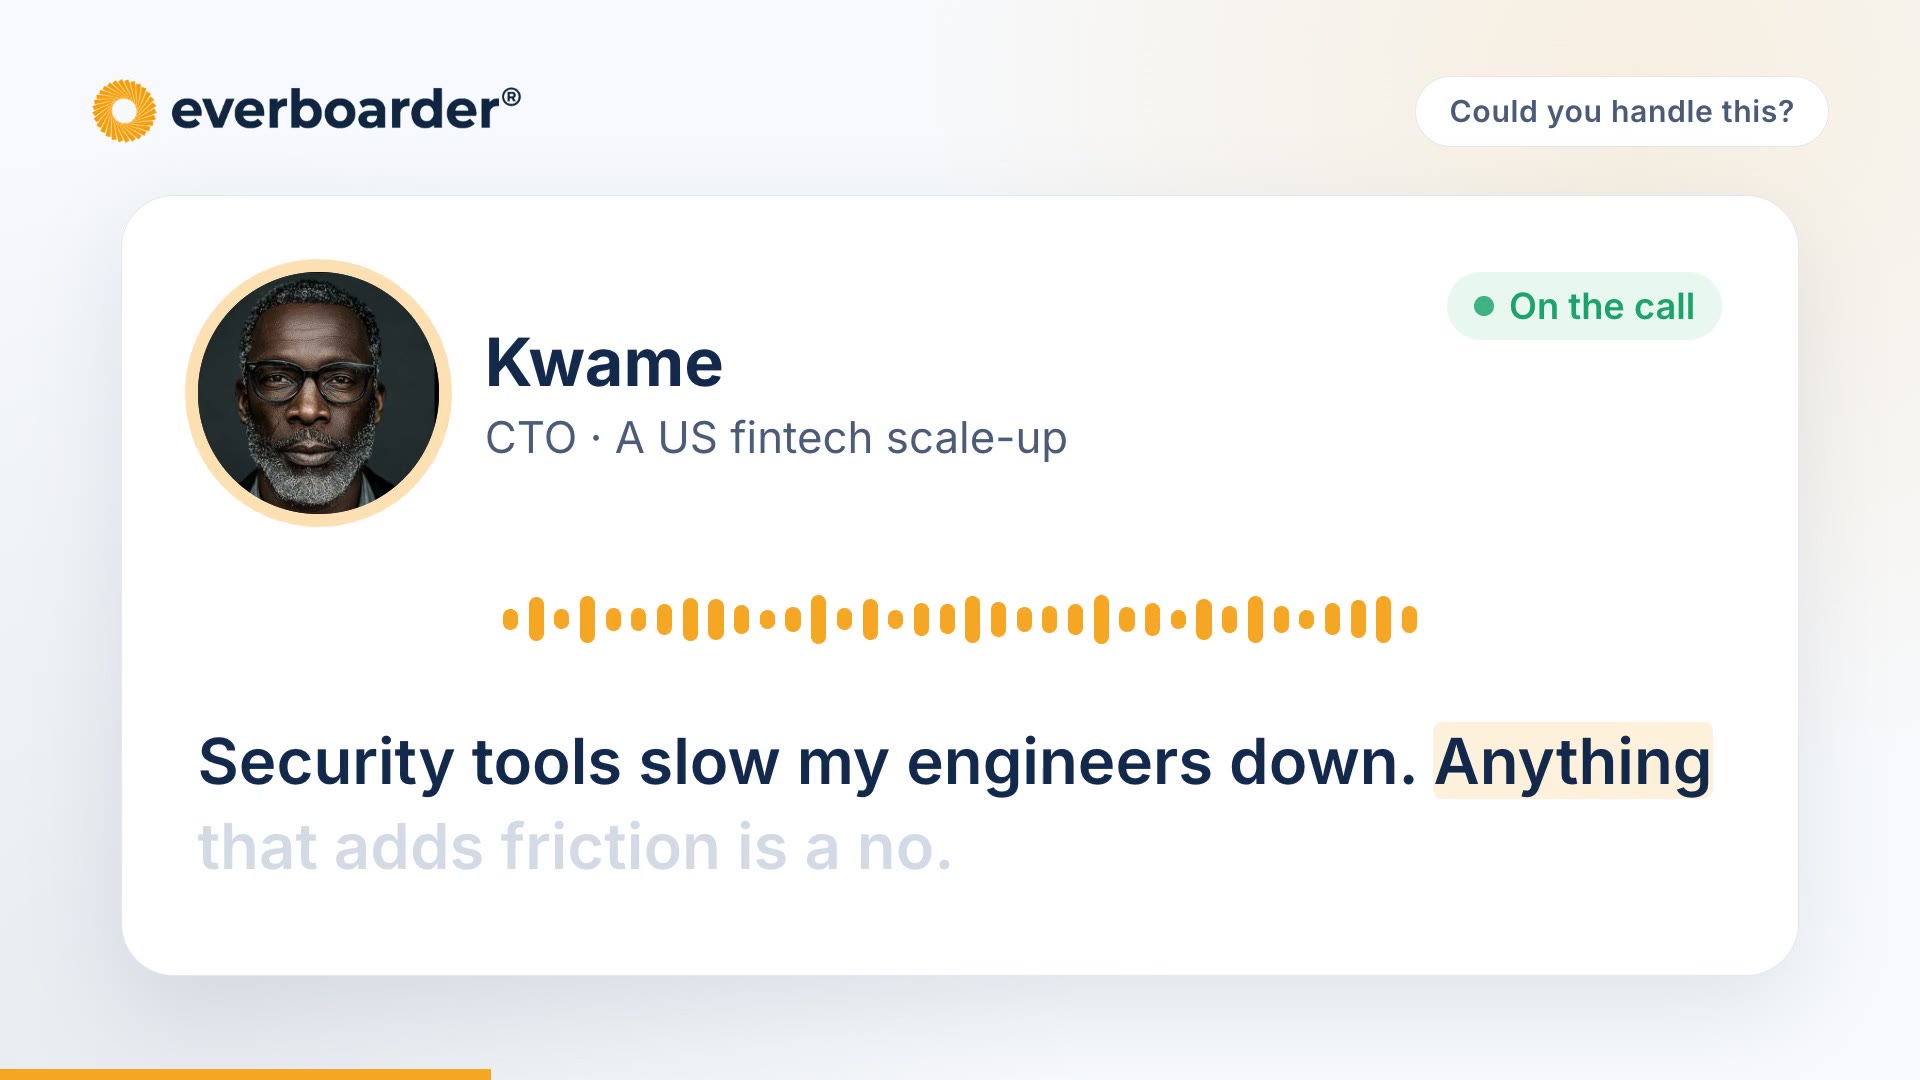
| “Security tools slow my engineers down” | CTO | Start with their goal. |
| “We're compliant, we passed our audit” | Head of Risk and Compliance | Separate compliant from secure. |
| “Our managed service provider handles it” | Head of IT | Find the edges of “covered”. |
| “Another tool just means more noise” | Head of Security Operations | Ask what gets missed. |
Watch all 6 objections
Practise these objections
Free to start. No credit card.